Structure Firewall Logs to Find Suspicious Access Faster and Build More Precise Alerts
"Did the firewall block this source when it accessed the new service?"
After a business release, network engineer Chen needs to answer a specific question: in the past 30 minutes, were there any deny records for source 198.51.100.23 accessing port 443 on service 192.0.2.80?
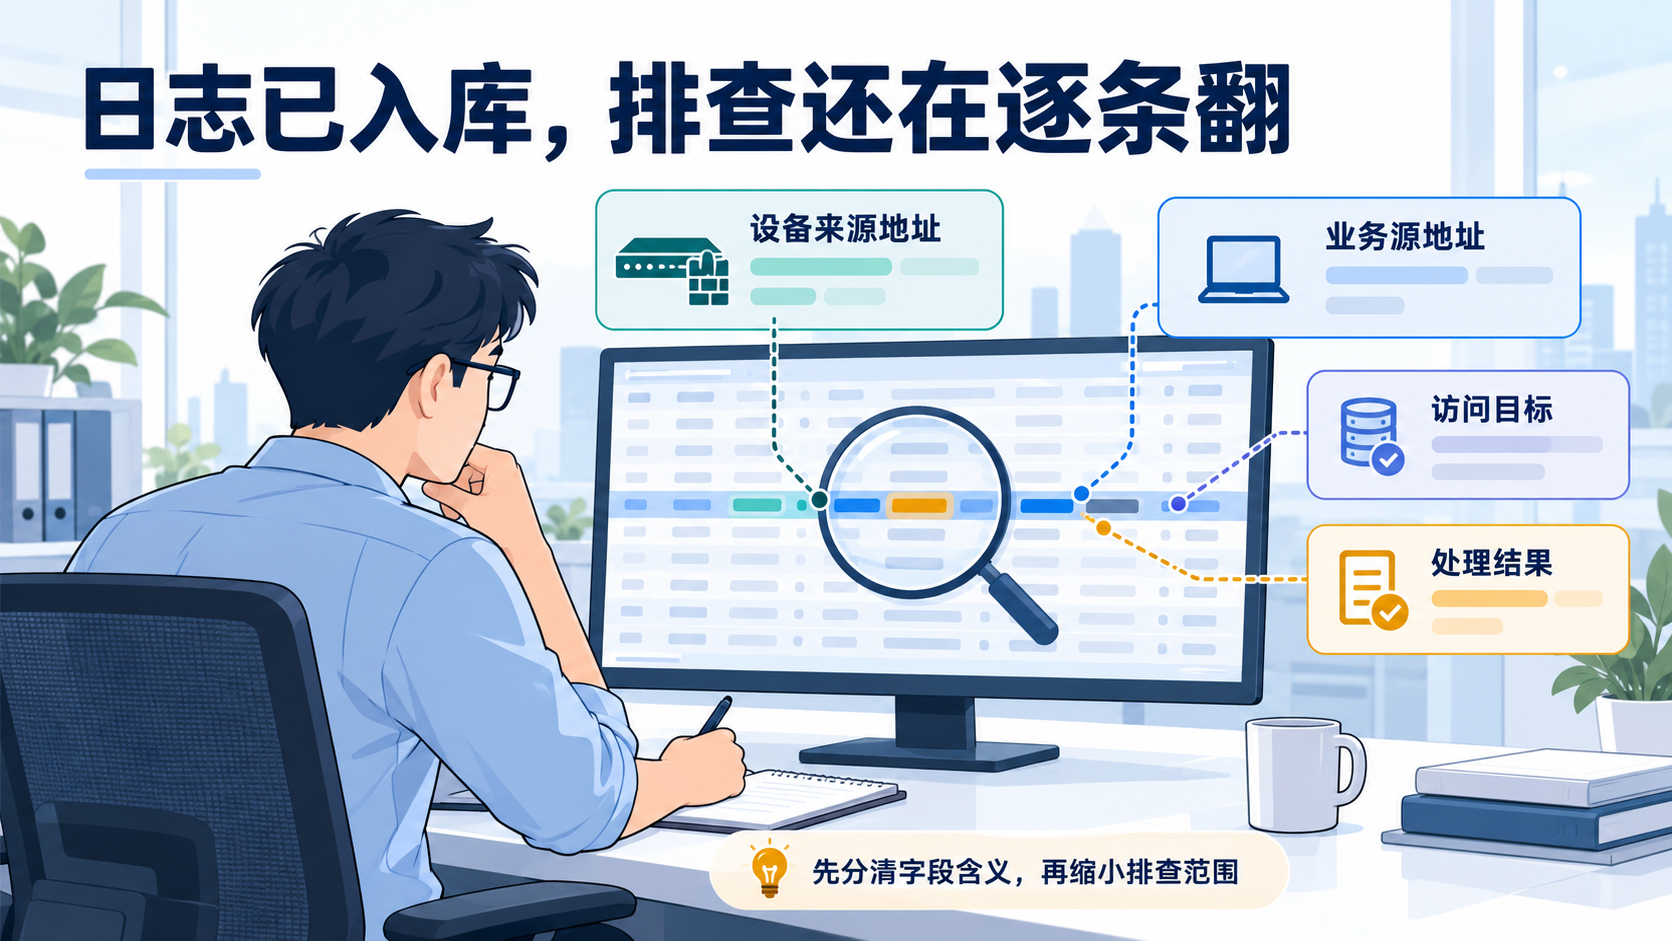
He has already centralized firewall logs in a search platform. Searching for the source IP returns results, but to answer the business team he still has to inspect each line to work out where the address appears, what the connection targets, and how the firewall handled it. When another colleague takes over, that interpretation often has to be repeated.
Structured firewall logs can reduce this repeated work: extract the access relationship from each raw message into fields, so a query can express the business question directly and the same conditions can be reused for alerts.
Let's follow this investigation to see how it works in practice. The addresses and log entries below are simplified examples.